Agentic AI Governance: 10 Runtime Controls Before Enterprise Agents Scale
A practical readiness guide for engineers, developers, and technology leaders moving enterprise agents from prototype demos to production control.
What must be controlled before an enterprise agent is allowed to act inside business-critical systems?
Agentic AI Governance becomes a runtime engineering problem once an AI agent can call APIs, update records, write to memory, and trigger workflows. In line with lifecycle risk management emphasized by the NIST AI Risk Management Framework, controls must operate where proposed actions become enterprise consequences.
Four distinctions frame this guide:
Ability is not authority. Authority is not legitimacy. Authorization is not execution. Execution is not evidence.
The 10 Runtime Controls identify what must be bounded, validated, monitored, or escalated before agents scale. The Four Runtime Governance Pillars provide the architecture for enforcing those controls before consequence, intervening when conditions change, recovering safely, and reconstructing what happened.
1. From Model Output to Governed Consequence
Enterprise risk does not begin when an AI model generates an answer. It begins when that answer is allowed to change enterprise state.
A typical agentic workflow may look like this:
Request → Agent reasoning → Proposed action → Governed execution boundary → Enterprise consequence
Before that boundary, the agent may retrieve evidence, select tools, plan steps, or recommend an action. At the boundary, however, the question changes from:
What does the agent want to do?
to:
May this exact consequence become real now?
Runtime governance verifies the upstream mandate behind authority; it does not create legitimacy.
At each consequential action or state transition, the system should evaluate:
State → Intent → Authority → Consequence → Admissibility → Binding Disposition
The decision resolves through one of five binding dispositions:
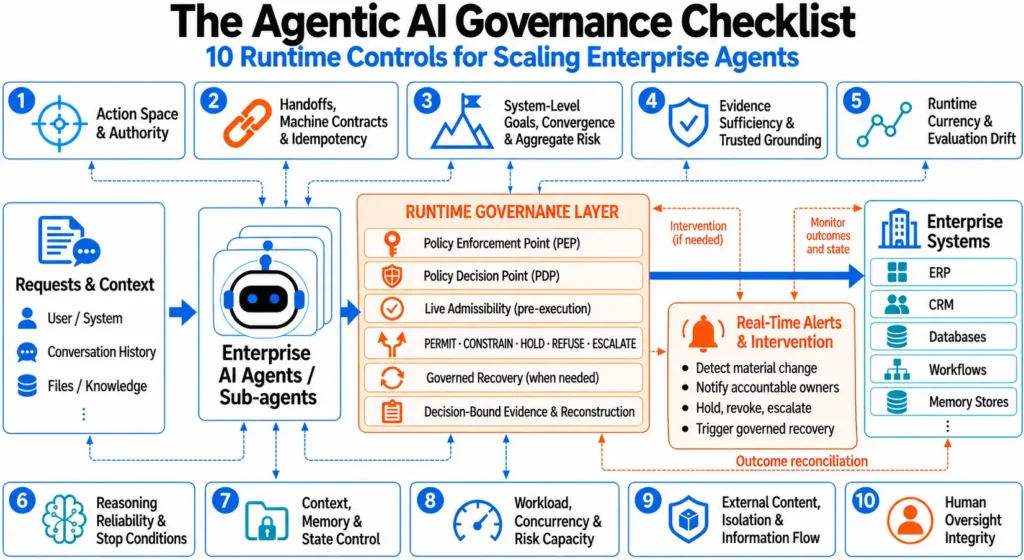
PERMIT · CONSTRAIN · HOLD · REFUSE · ESCALATE
PERMIT allows the action to proceed. CONSTRAIN permits only a bounded form. HOLD pauses execution while a material condition remains unresolved. REFUSE blocks the action. ESCALATE routes the decision to an authorized reviewer or higher authority without granting execution permission.
Prior approval, valid credentials, successful testing, or technical capability do not create continuing permission to execute. Authority, evidence, workflow state, policy, and the realized execution plan may all change before consequence.
The agent proposes. Governance determines whether the consequence may become real.
2. The 10 Runtime Controls for Enterprise Agents
The following controls translate runtime governance into practical engineering questions. They do not replace the Four Runtime Governance Pillars. They identify what must remain controlled before enterprise agents create consequential state changes.
1️⃣ How large can the agent’s action space and authority become?
As agents gain access to more tools, APIs, databases, and workflows, both capability and possible execution paths expand. If an agent has k tools and may take up to d sequential steps, possible trajectories can grow approximately as O(k^d).
But capability does not equal authority. Tool access must remain bounded by purpose, scope, target, validity period, and revocation status.
Delegation can only preserve or narrow authority, never expand it. Further delegation to sub-agents must be explicitly permitted and bounded by purpose, scope, duration, depth, fan-out, and aggregate exposure.
For higher-consequence actions, logical agent identity is also insufficient by itself. The execution boundary should bind the authorized agent to the actual workload or process instance and its current trust domain before effect.
Engineering controls: Execution-depth limits, tool-call limits, least privilege, delegation attenuation, runtime-instance binding where material, validity windows, revocation checks, loop detection, and mandatory interception of effectful actions.
Governance question: Can the agent perform this action, and does it still have authority to create this exact consequence now?
2️⃣ Can a handoff remain valid across agents, tools, and state changes?
A syntactically valid handoff may still be operationally invalid. Valid JSON does not guarantee valid business meaning.
The receiving system must verify machine-contract compliance, preserve what was actually reviewed, prevent duplicate effects, and determine what already executed before retrying or recovering.
A missing acknowledgment is an unresolved state, not proof that nothing happened.
This distinction between interface validity and execution validity is developed further in the ERP-Agent Bridge.
A handoff crossing a trust or deployment boundary should trigger revalidation rather than automatically inherit upstream assurance. Shared-state execution integrity is addressed in Control 5.
Engineering controls: Schema and semantic validation, authenticated handoffs, decision-context binding, machine-contract checks, replay protection, idempotency, acknowledgment reconciliation, residual-state assessment, and recovery admission.
Governance question: Does the next step verify what was authorized, what already happened, and whether continuation remains admissible?
3️⃣ Can individually valid agents create an unacceptable system-level result?
Multi-agent systems can fail even when each agent appears locally correct. Agents may optimize different objectives, compete for resources, or collectively exceed financial exposure, institutional risk capacity, or authority concentration.
Fragmentation creates another risk. An action exceeding a threshold may be divided across agents or requests, each below the individual limit. Individually admissible fragments must not authorize a jointly prohibited purpose or aggregate-bound violation.
During recovery, one agent’s state change may invalidate another agent’s concurrent revalidation. Agreement among agents also does not establish independent evidence when their conclusions rely on the same source or correlated failure conditions.
A versioned interaction profile should identify participating agents, shared resources, delegation paths, and collective decision roles. Governance must evaluate both individual decisions and their combined consequences.
Engineering controls: Shared objectives, workflow-level KPIs, interaction profiles, cumulative-exposure monitoring, concurrency contracts, risk-capacity reservation, dependency-aware revalidation, collective-evidence checks, and convergence monitoring.
Governance question: Do local decisions, concurrent actions, recovery paths, and agent interactions remain acceptable when evaluated as one enterprise system?
4️⃣ Is the agent’s decision supported by sufficient, current evidence?
Enterprise action requires more than a plausible answer or citation. The system should know where decision-relevant evidence originated, whether it is authoritative and current, and whether it is sufficient for the proposed consequence.
Evidence provenance is not evidence sufficiency, and evidence sufficiency does not guarantee representation adequacy.
A trusted source may still be incomplete or fail to represent a material condition. Evidence should support only the proposition actually established.
For consequential decisions, governance should also identify missing observations, contradictory sources, and material uncertainty rather than treating available information as necessarily complete.
Engineering controls: Source ranking, provenance capture, freshness checks, evidence-sufficiency rules, representation-adequacy checks, independent observation where required, and escalation when material evidence is missing.
Governance question: Can the system show that evidence is current and sufficient and that the governed representation captures the material conditions relevant to this decision?
5️⃣ Are the assumptions that justified approval still valid at execution time?
An agent can become inadmissible even when the model has not changed. APIs, permissions, evidence, workflow state, targets, reviewer authority, policy activation, or business conditions may drift between evaluation and execution.
Predeployment tests, red-team results, certifications, and prior successful runs are supporting evidence, not continuing runtime permission.
Premise age includes inference, queuing, human review, retry, and dispatch delays. A material change invalidates a premise regardless of elapsed time.
For shared-state actions, revalidation alone is insufficient. Validation must be bound to the actual effect through a transaction, compare-and-set, fencing, or equivalent mechanism that prevents material state changes between check and commit.
This is particularly important when several agents act concurrently on shared enterprise resources.
Engineering controls: Version and activation-state tracking, validity horizons, latency-aware freshness, authority and evidence revalidation, authenticated Governance Status Signals, execution-scope continuity, check-to-commit binding, and material-change triggers.
Governance question: Are the authority, evidence, assumptions, policies, and execution scope that justified the action still valid now?
6️⃣ When should the agent stop reasoning and enter a governed disposition?
More reasoning does not always produce a better decision. Repeated loops, contradictions, weak evidence, unstable plans, or excessive uncertainty should not silently lead to execution.
When a defined threshold is crossed, the system should resolve the case through HOLD, CONSTRAIN, REFUSE, or ESCALATE rather than allow indefinite autonomous reasoning. CONSTRAIN is available only when a bounded alternative is explicitly authorized and remains admissible.
Engineering controls: Reasoning-depth limits, contradiction detection, evidence thresholds, timeout rules, uncertainty triggers, fallback paths, and risk-based escalation.
Governance question: Does the agent know when continued reasoning no longer justifies autonomous progression?
7️⃣ Can context, memory, or prior state change what the agent is allowed to do?
Large context windows do not solve governance. Important constraints may be buried, persistent memory may become stale, and earlier actions may change what remains permissible.
Memory writes should therefore be treated as governed state changes.
Decision-relevant execution history should also carry forward, including prior tool calls, sensitive access, dispositions, exceptions, credential use, and exposure to untrusted content.
When a material dependency becomes invalid, subsequent decisions relying on it require renewed evaluation rather than treating accumulated context as automatically trustworthy.
Engineering controls: Context boundaries, memory-write controls, state validation, external policy enforcement, temporal metadata, governance-context accumulation, dependency tracking, and revalidation after material state changes.
Governance question: Does the runtime architecture preserve the state needed to decide whether the next action remains admissible?
8️⃣ Can the system handle peak workload without exceeding governance capacity?
Production agents operate under concurrency, queueing, rate limits, approval delays, and shared infrastructure.
Little’s Law remains useful:
L = λW
where L is average active work, λ is the arrival rate, and W is average time in the system.
Governance has capacity limits too. Reviewer queues can grow, approvals can expire while waiting, and simultaneous actions can consume bounded risk capacity.
Reviewer overload must never convert an unreviewed action into PERMIT or justify reusing stale approval.
Likewise, sufficient processing capacity does not guarantee that concurrent actions preserve shared-state invariants or aggregate-risk limits.
Engineering controls: Load testing, queue monitoring, tail latency, concurrency limits, backpressure, shared-risk-capacity reservation, conflict detection, reviewer-capacity monitoring, and governed HOLD, REFUSE, or ESCALATE behavior when decision infrastructure is unavailable.
Governance question: Does the system remain controlled when agents, reviewers, and consequential actions compete for the same resources?
9️⃣ Is untrusted content isolated from instructions, tools, and external destinations?
Enterprise agents process emails, PDFs, webpages, files, tool output, persistent memory, and peer-agent messages.
These may inform reasoning, but they remain data. They must not create, widen, renew, or substitute governance authority through model interpretation alone.
Any transition from untrusted data into governance control should pass through an independently governed authority path.
Risk also arises when individually permitted capabilities combine into an unsafe path, such as sensitive-data access plus untrusted content plus external communication.
Engineering controls: Content labeling, sandboxing, tool separation, allowlists, least privilege, egress and information-flow controls, and constrained execution.
Governance question: Can untrusted information influence reasoning without acquiring authority over execution or information flow?
🔟 Can human oversight remain authoritative and meaningful?
Human approval does not automatically make an agent safe. Oversight is dependable only when the reviewer has verified identity, appropriate authority, sufficient competence, manageable workload, access to relevant evidence, and the practical ability to intervene before consequence.
This is especially important in human-agent workflows, where poor design can turn meaningful oversight into routine rubber-stamping.
Refusal, abstention, timeout, nonresponse, and failed decision-capture events must not be interpreted as approval.
If an earlier approval becomes stale and the original reviewer is unavailable, it must not be reused automatically. The action remains on HOLD while substitute authority is verified. If no valid approval path is established within the applicable deadline, the predefined REFUSE or ESCALATE path applies, except for an explicitly preauthorized constrained alternative.
Engineering controls: Reviewer-authority verification, workload limits, evidence-rich review, positive and negative decision logging, timeout handling, substitute-authority rules, and escalation paths.
Governance question: Is the reviewer genuinely able and authorized to change what happens next?
3. Industry Control Profiles: Why Runtime Controls Change by Application Area
The 10 runtime controls provide a common engineering backbone, but they should not carry identical thresholds in every application area.
| Industry / Application | Stronger Runtime Emphasis |
|---|---|
| Finance | Authority, idempotency, transaction limits, aggregate exposure |
| Healthcare | Evidence sufficiency, human oversight, current context |
| DevOps | Isolation, permissions, rollback and recovery |
| Manufacturing / Logistics | System-level goals, concurrency, operational resilience |
A versioned domain profile translates stable governance principles into application-specific thresholds, evidence classes, decision rights, validity horizons, aggregate-risk limits, isolation requirements, recovery paths, and escalation rules.
Risk tier should therefore be assigned to the proposed consequence, not merely to the tool, model, or application category.
The Four Runtime Governance Pillars framework uses four consequence tiers: T0 Observational, T1 Reversible Bounded Action, T2 Consequential State Mutation, and T3 High-Consequence/Low-Reversibility, with progressively stronger runtime assurance and enforcement.
In multi-agent deployments, consequence assessment also considers delegated authority, shared dependencies, cumulative exposure, and propagation potential.
The architecture remains consistent; the control profile changes with the consequence.
4. Governance Readiness Is Not Runtime Admissibility
The 10 runtime controls can be scored from 1 to 5 to show where an enterprise agent is strong, weak, or still dependent on prototype safeguards.
| Score | Governance Maturity |
|---|---|
| 1 | No clear control |
| 2 | Basic or mostly manual control |
| 3 | Tested in limited conditions |
| 4 | Production-ready control |
| 5 | Continuously governed and revalidated |
The score measures governance maturity. It does not authorize a particular action.
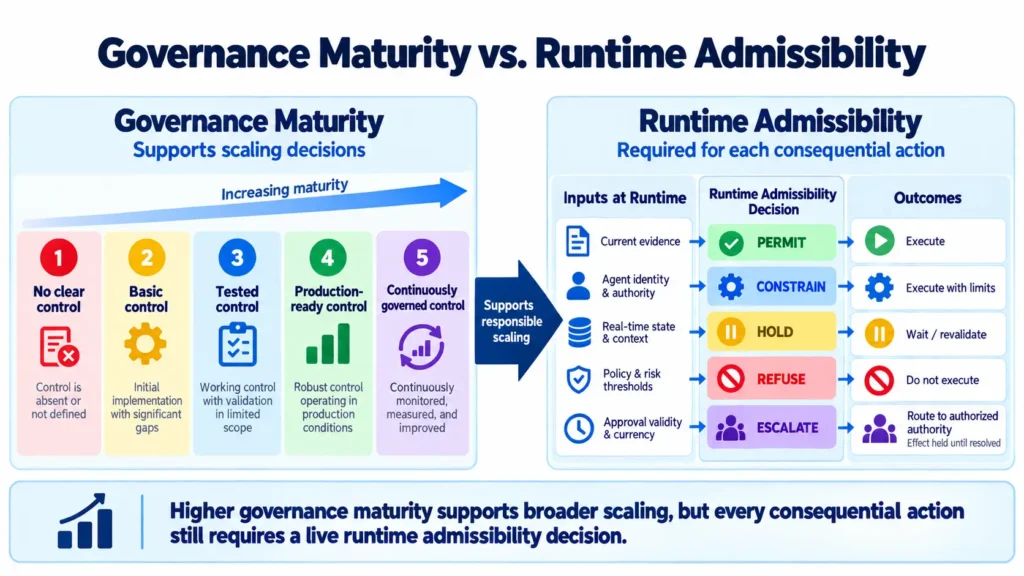
The maturity score can inform deployment scope, supervision, monitoring intensity, and improvement priorities. Live execution still requires a current admissibility decision.
Minimum Viable Runtime Governance Profile
Before scaling beyond read- or recommend-only use, an enterprise system should have a minimum runtime governance control spine:
- Authority and profile controls: Identify the sponsoring principal, logical agent, and owner/lifecycle state; resolve current authority from authoritative sources rather than self-assertion; use a versioned domain profile; and maintain current permit and activation-epoch standing.
- Mandatory enforcement: Every consequential effect passes through an identified governed control surface, with authorization logic independent of the model and bypass prevented.
- Live admissibility: Decisions resolve through PERMIT, CONSTRAIN, HOLD, REFUSE, or ESCALATE. Unresolved, stale, contradictory, unavailable, or materially under-represented conditions never default to PERMIT.
- Execution integrity: Current scope, evidence, policy/profile state, replay protection, idempotency, relevant execution history, and material shared-state dependencies are validated before consequence.
- Decision evidence: Positive and negative decisions are durably recorded and linked to execution receipts, including relevant dependency and effect evidence.
- Change and recovery: Material authority, epoch, reviewer, credential, trust, or dependency changes propagate to dependent execution and trigger HOLD or re-admissibility within a defined latency objective. Containment, governed recovery, and reconstructable records remain available.
For multi-agent deployments, the profile should also identify consequential interactions, shared-state dependencies, collective-risk constraints, and the mechanisms binding validation to execution.
Risk-tier requirements may be stronger than this baseline.
An average score cannot compensate for a missing minimum or domain-critical control. If the applicable MVP or risk-tier requirement is not satisfied, the score does not authorize scaling.
| Average Score | Indicative Deployment Posture |
|---|---|
| 1.0–2.4 | Not ready to scale |
| 2.5–3.4 | Limited pilot candidate |
| 3.5–4.4 | Controlled production candidate |
| 4.5–5.0 | Broader scaling candidate |
Maturity informs scaling. Runtime admissibility authorizes action.
5. Developer Implementation Pattern: Governance as Runtime Infrastructure
The 10 runtime controls matter only if they are enforced in the execution path. An enterprise agent may propose, plan, and orchestrate, but it should not authorize its own consequential behavior.
A practical runtime pattern is:
Agent proposes → Policy Enforcement Point intercepts → Policy Decision Point evaluates → Binding disposition → Execution → Outcome reconciliation
The Policy Enforcement Point (PEP) is the mandatory enforcement point. It intercepts the proposed effect and obtains a binding decision from an independently governed Policy Decision Point (PDP).
The PEP-PDP exchange should use an explicit Governance Decision Contract that binds decision-relevant identity, authority, action, target, context, evidence, profile, activation epoch, constraints, validity, and revalidation conditions to the disposition.
A consequential effect surface without an identified governed enforcement path should fail closed.
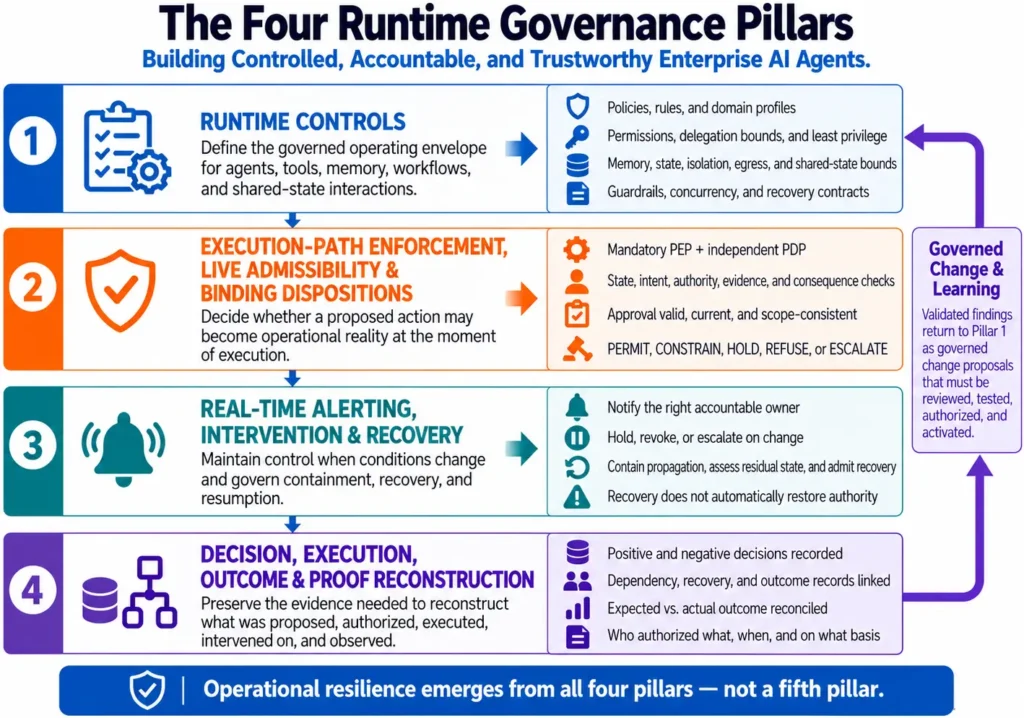
The Four Runtime Governance Pillars organize this architecture across three planes:
- Specification & Control Plane (Pillar 1): Defines governance requirements and operating boundaries.
- Runtime Decision & Response Plane (Pillars 2–3): Enforces admissibility, intervention, and governed recovery.
- Assurance & Learning Plane (Pillar 4): Reconstructs evidence, verifies outcomes, and produces bounded findings for improvement.
Findings from Pillar 4 do not directly modify runtime policy. They return to Pillar 1 as change proposals that must be reviewed, tested, authorized, and activated before changing the runtime baseline.
Pillar 1: Runtime Controls
Defines the governed operating envelope before consequence. It establishes identity and authority requirements, domain profiles, tool and memory boundaries, isolation and egress rules, risk limits, and enforcement, evidence, interaction, and recovery contracts.
For multi-agent systems, these include delegation bounds, concurrency contracts, collective-risk limits, and shared-state requirements.
Pillar 2: Execution-Path Enforcement, Live Admissibility & Binding Dispositions
Determines whether a proposed consequence may become operationally real under current conditions.
It verifies authority, evidence, scope, policy, state, risk, and applicable concurrency constraints; issues one of five binding dispositions; enforces the decision; and binds it to evidence for later verification.
Technical capability or prior approval does not substitute for current admissibility.
Pillar 3: Real-Time Alerting, Intervention & Recovery
Maintains control when material conditions change. It detects invalidated assumptions, triggers HOLD or re-admissibility, contains propagation, and governs recovery.
When relied-upon state, evidence, or tool results are invalidated, dependent pending effects must be blocked and re-admitted. Already committed effects require residual-state assessment rather than automatic rollback.
Material repair, substitution, or compensation constitutes a new consequential proposal requiring admission through Pillar 2. A repaired final state cannot legitimize an unauthorized intermediate effect.
Technical recovery does not automatically restore authority. This process is developed further in Agentic AI Operational Resilience: Recovering Safely and Restoring Admissible Operation.
Pillar 4: Decision, Execution, Outcome & Proof Reconstruction
Preserves, correlates, and verifies the evidence needed to reconstruct what was proposed, authorized, enforced, executed, intervened on, and observed.
It connects decision evidence with execution, intervention, recovery, dependency, and outcome records. Validated findings become governed improvement proposals for Pillar 1 rather than automatic policy changes.
Agent proposes. Governance authorizes. Execution remains conditional on current admissibility.
This is what turns Agentic AI Governance from a policy checklist into enforceable runtime infrastructure.
6. Conclusion: Scaling Agents Requires Measurable Control
Before enterprise agents scale, organizations should demonstrate bounded action space, current authority, sufficient evidence, valid handoffs, safe reasoning limits, controlled concurrency, effective information boundaries, and meaningful human oversight.
Multi-agent execution adds further obligations: collective admissibility, shared-state integrity, dependency revalidation, and independent evidence where required.
But readiness is not runtime permission. Every consequential action still requires a live decision under current authority, evidence, scope, policy, state, and risk.
The Four Runtime Governance Pillars provide the operating structure to define controls, enforce admissibility, intervene and recover, and reconstruct what happened.
The ultimate test of Agentic AI Governance is whether an enterprise can control, authorize, recover, and prove the consequences of agent action.